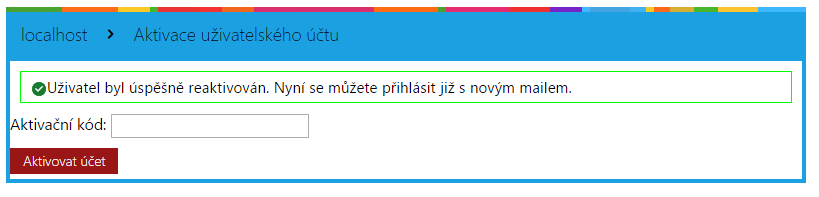
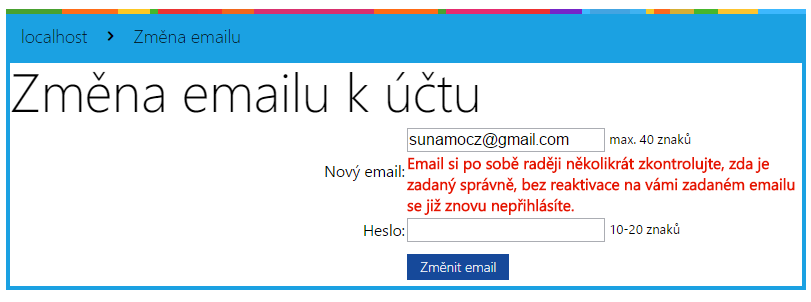
Until now, if an attacker wanted to change a user’s email so that the user could no longer log in, all they had to do was get to a computer where the victim was logged in and type in a new email. Now they will also have to enter the user’s current password. Of course, if users are careless and type in the wrong email, they won’t be able to reactivate their account and log in, and in that case even this security measure will be of no use to them. Screenshots of this feature: 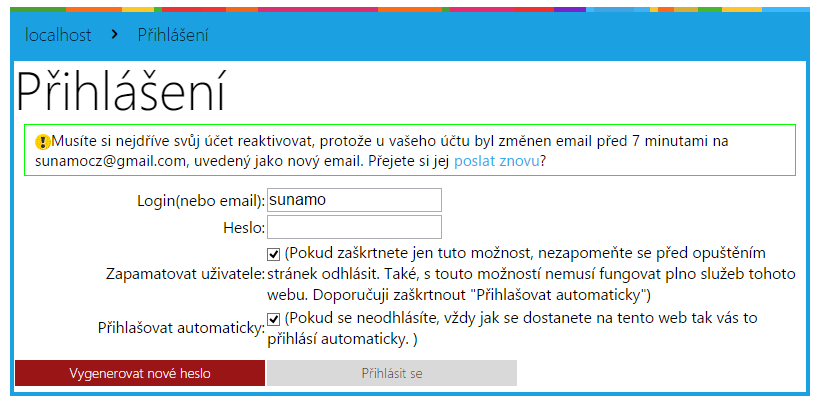
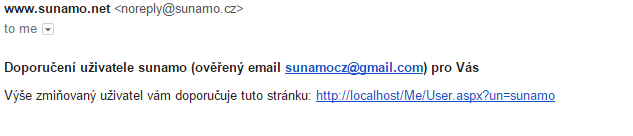
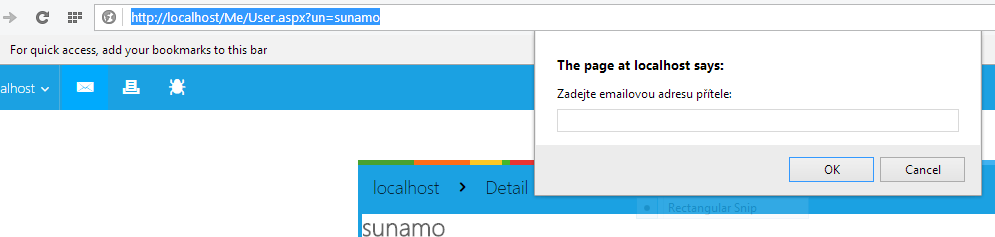
The second feature is sending a page to a friend. On any page of sunamo.cz/.net, just click the email icon in the top bar, enter the address you want to recommend the page to in the pop-up dialog, and you will then simply be told whether the email was sent. Again, a few explanatory screenshots:
Next, I’d like to optimize the Kocicky website, because pages load quite slowly. First and foremost, that means storing long texts together with the other data in the database (a leftover from the days when I stored large data in separate .txt files, and therefore with separate methods), and above all writing view statistics directly into the tables I take the data from.
Right now I have universal tables where I record and retrieve the view count with a single method, but because there are so many pages, the site keeps getting slower and slower.